Inner Range confirms products are unaffected by recently identified PHP vulnerabilities
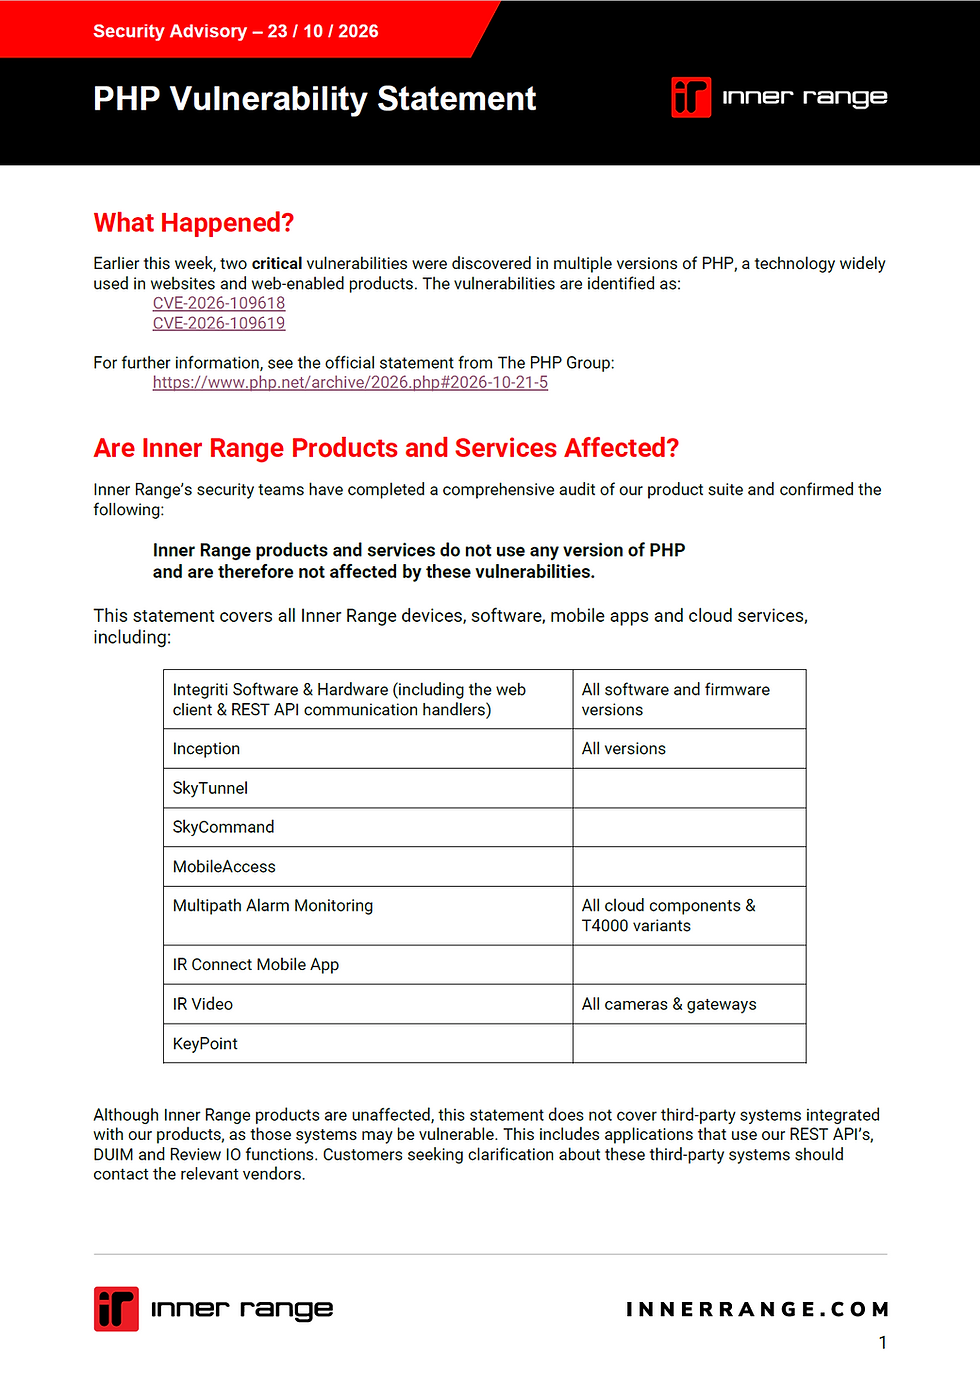
Two critical vulnerabilities have recently been identified in multiple versions of PHP, a technology widely used across websites and web-enabled products.
The vulnerabilities are identified as CVE-2026-109618 and CVE-2026-109619.
Following the disclosure, Inner Range security teams conducted a comprehensive audit of the Inner Range product suite to determine whether any products or services could be affected.
The audit confirmed that Inner Range products and services do not use any version of PHP and are therefore not affected by these vulnerabilities.
Which Inner Range products are covered?
The assessment covers Inner Range devices, software, mobile applications and cloud services, including:
Integriti Software & Hardware, including the web client and REST API communication handlers (All software and firmware versions)
Inception (All versions)
SkyTunnel
SkyCommand
MobileAccess
Multipath Alarm Monitoring (All cloud components & T4000 varients)
IR Connect Mobile App
IR Video (All cameras & gateways)
KeyPoint
What about third-party integrations?
While Inner Range products and services are unaffected, organisations should be aware that this assessment does not extend to third-party systems integrated with Inner Range products.
This includes third-party applications that use Inner Range REST APIs, DUIM and Review IO functions. These external systems may use PHP independently and therefore need to be assessed by their respective vendors. Customers with questions about a third-party product or integration should contact the relevant vendor for clarification.
What this means for Inner Range customers
For Inner Range customers and partners, the outcome is straightforward: Inner Range products and services are not affected by these PHP vulnerabilities.
Where Inner Range products are connected to third-party systems, customers should check with the relevant vendor regarding the security status of those systems.
For further information contact Inner Range directly.